Starbucks, Expedia among companies targeted by Russian cyberattackers
Published in Business News
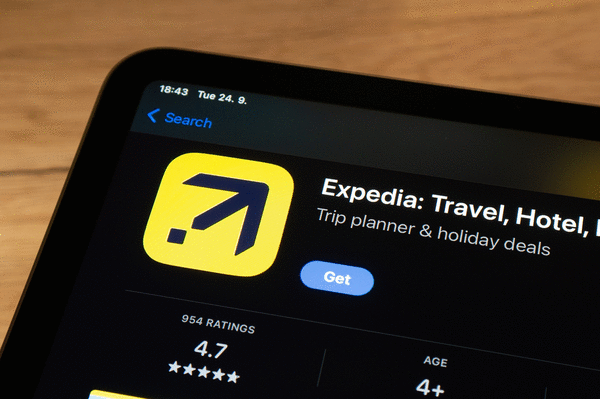
Expedia Group and other major companies worldwide have allegedly suffered cyberattacks from an extortion group based in Russia, leaving user data potentially at risk.
The group, known as n0n, claimed responsibility for the breaches, according to multiple news outlets.
Expedia told The Seattle Times on Wednesday that it was “aware of a supply chain attack, reported by security researchers, in which attackers compromised a third-party data platform provider and used its trusted access to reach systems at multiple companies, including Expedia Group.”
The Seattle-headquartered travel technology company said it is actively investigating the breach. Its most well-known brands include Expedia, Hotels.com and Vrbo.
In recent days, a list from cybersecurity firm SOCRadar also showed Starbucks among 192 organizations across 51 countries that possibly fell victim to the cyberattacks. But the Seattle-based coffee giant said Wednesday it had “found no evidence of unauthorized access” to its network or systems.
Starbucks said the claims it investigated focused on “unauthorized access to a limited amount of industry advertising information about Starbucks customers.”
The cyberattack on Expedia was previously reported by travel industry news source Skift.
In Expedia’s case, n0n allegedly exposed a data set spanning 500 megabytes, consisting of millions of customer travel records, per cybersecurity outlet Cybernews.
“These are unverified claims from criminals,” Expedia said, “and we cannot confirm their accuracy.”
Law firm Ahdoot & Wolfson is exploring a potential class-action suit against Expedia after the attack. It said the filched information allegedly spanned traveler profile information, customer email addresses, loyalty program member IDs, points balances, membership tier details and booking values.
“We take our travelers’ privacy extremely seriously,” Expedia said. “Our platforms remain safe to use for both travelers and partners.”
In September, n0n publicly emerged on the darknet, according to cybersecurity research organization FortiGuard Labs. It’s also known by aliases OWN3R_AN0NYM0US, An0nyByte, n0n Ransomware Group and more.
The group tends to zero in on sectors like defense, government and technology for the purpose of extorting money after stealing data.
“n0n shows no ideological, hacktivist or state-directed motive,” according to SOCRadar. “Every demand is financial, and target selection favors organizations whose compromise causes the most operational damage.”
The group typically demands bitcoin payments from targeted companies, setting up a deadline to receive the money before moving forward with leaks.
©2026 The Seattle Times. Visit seattletimes.com. Distributed by Tribune Content Agency, LLC.
Comments